A factual look at ChatGPT Atlas privacy, the 7-day server retention window for browser memories, and how to manage your digital footprint safely.
This article was researched and drafted with AI, then checked and released by a person before it went live. The illustration is AI-generated. Every factual claim links to its source, so you can verify it yourself.
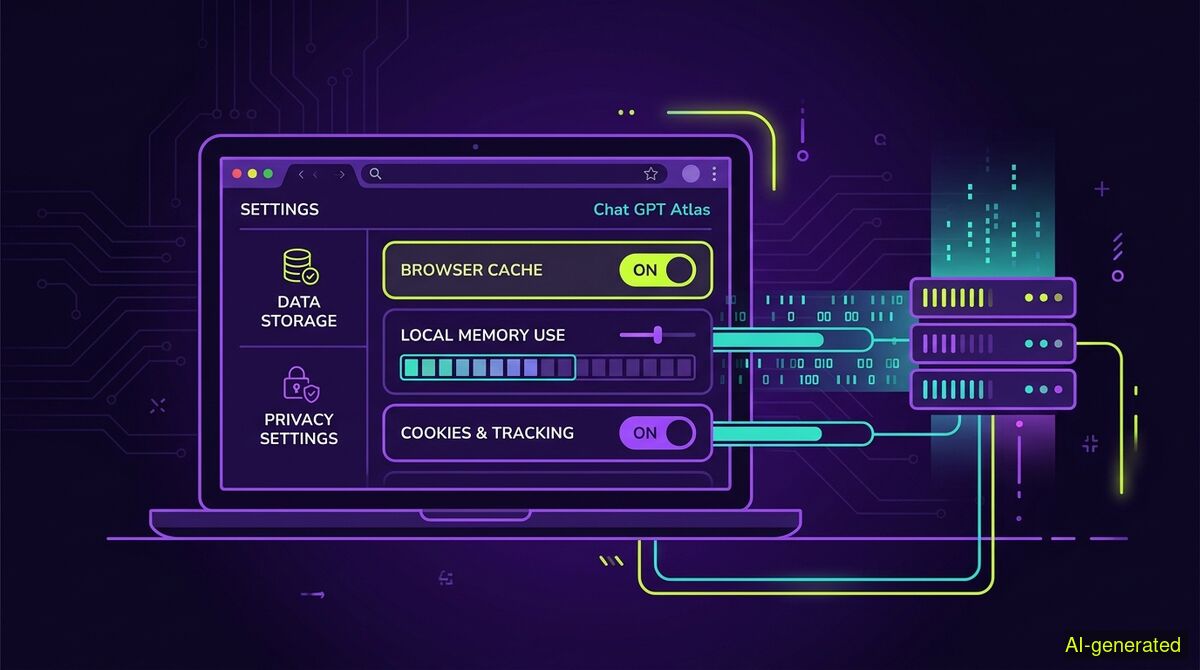
AI-generated illustration. A laptop screen showing a browser settings menu with memory and privacy toggles next to a server icon.
ChatGPT Atlas stores your browsing actions and website context as memories on OpenAI servers for up to seven days. While the browser offers agentic automation, security researchers have identified vulnerabilities that allow malicious prompt injections into these persistent memories. You can manually delete your conversations, but third-party tools cannot bypass the server retention window.
When OpenAI launched a web browser built directly around its artificial intelligence models, it fundamentally changed how web navigation works. Instead of merely rendering web pages, the software is designed to read them, understand your context, and complete multi-step tasks on your behalf. This shift in functionality has led many users to search for chatgpt atlas privacy to understand exactly what data leaves their machine. The answer involves persistent server storage, new types of security vulnerabilities, and a fundamental trade-off between convenience and data collection.
Understanding whether this browser is safe requires looking at its underlying architecture. Traditional browsers pull data from the internet to your screen. Agentic browsers like Atlas read your screen and send that context back to a server to decide what to do next. This requires a level of telemetry that goes far beyond standard cookies or browsing history.
Most web browsers on the market today are passive tools. They wait for you to type a URL or click a link, and then they fetch the requested data. According to a broadcast by NPR, Atlas operates differently by incorporating an "agentic mode". This means the browser can take control of the navigation process to complete tasks across the web without you needing to copy and paste information between tabs.
To achieve this level of automation, the artificial intelligence must constantly monitor your active window. It needs to know what text is visible, what buttons are available, and what you have already done on the page. This is not a local process. The browser streams this context to OpenAI servers to process the visual and textual data, formulate a plan, and send back execution commands.
The core privacy concern with Atlas stems from how it retains the context of your browsing sessions. As the Washington Post reported, Atlas out-surveils traditional browsers like Google Chrome by storing "memories" of what you look at and do on specific websites. It does not just log the fact that you visited a domain. It records the interactions you had there.
These memories are designed to make future interactions smoother. If you frequently check specific data or perform repetitive tasks, the AI remembers your preferences and past actions. However, this means your browsing habits, the content you read, and the actions you take are aggregated into a persistent profile tied to your OpenAI account.
For enterprise environments, the rules differ slightly. According to the OpenAI Help Center, access to Atlas for Enterprise workspaces is turned off by default. Workspace owners must actively enable it, allowing teams to evaluate the browser with low-risk data in a beta environment before deploying it across a company. For consumer accounts, however, this data collection is an inherent part of using the software.
Storing browsing context as persistent AI memories introduces entirely new attack vectors that traditional browsers do not face. Shortly after the browser launched, security vendor LayerX discovered a vulnerability they named "ChatGPT Tainted Memories".
The researchers found that bad actors could exploit a cross-site request forgery flaw to inject malicious instructions directly into the AI's memory. Because the memory is persistent, these malicious instructions survive across different browsing sessions. As noted by The Register, this exploit requires a user to click a malicious link. Once clicked, the hidden instructions are planted in the browser's memory.
The danger of this vulnerability is profound. If the AI is later given a task, the tainted memory can trick the agent into executing malicious code, granting access privileges to the attacker, or deploying malware. Furthermore, LayerX reported that the browser lacked meaningful anti-phishing protections at launch, making users highly vulnerable to these specific types of attacks. Axios also highlighted concerns from security researchers regarding prompt injections, where attackers hide commands in normal-looking websites or emails to manipulate the AI into violating its own safety rules.
A common misconception is that deleting a chat thread instantly erases all traces of that interaction from OpenAI servers. In reality, server-side telemetry and browser memories operate on strict retention schedules. According to OpenAI documentation, these system memories and telemetry logs remain on their servers for up to seven days.
This retention window is absolute. You can manually delete your conversations within the ChatGPT interface, but you cannot force the servers to purge the underlying telemetry data any faster. No third-party privacy tool, cleaner, or extension can reach into OpenAI's infrastructure to erase these browser memories.
Because agentic browsers read everything on your screen to build their context, your public social media feeds become part of the data they ingest. If you browse your old X or Instagram profiles using an AI-integrated browser, the software processes those historical posts, replies, and likes as part of its working memory.
To limit what AI systems can learn about you from your own profiles, you have to manage the source data. This means actively cleaning up your public footprint on the platforms themselves. Third-party tools cannot clear your Atlas browser memories, but they can help you remove the social media content that feeds into those memories.
If you choose to clean up your public profiles, you can do so manually by deleting posts one by one in the native apps. Alternatively, you can use the wyper Social Cleanup extension to automate the process. The extension operates strictly on X and Instagram. It can clear posts, replies, comments, likes, and reposts, as well as handle unfollowing and removing followers.
It is important to understand how the extension filters content. There is no date filter and no date range option available. If you want to isolate specific posts, you must use the keyword filter. This allows you to delete only items containing a specific word, a username, or a hashtag. You can separate multiple keywords with commas, and there is an INVERT option that deletes everything that does not contain your chosen keyword.
The extension requires no password, no API key, and no OAuth authorisation. Its only browser permissions are storage and activeTab, meaning it acts only in the tab you already have open while logged in as yourself. This design choice is a direct trade-off: because the tool holds no authorisation keys, it cannot delete on a schedule or run in the background while you are away. Competing services can perform background scheduling precisely because the user granted them standing account access and they run on external servers. The wyper extension cannot run without an open tab, because it never asks for the keys to your account.
Both the manual route and the wyper extension are irreversible. Once a post or reply is deleted from X or Instagram, it cannot be restored. The wyper free tier allows 50 deletions per day, while the Pro tier removes this limit and provides a deletion receipt featuring counts and a shareable proof link. During particularly long deletion runs, the extension can display small games in the interface while it works through your list.
| Feature | Manual cleanup | wyper Social Cleanup extension |
|---|---|---|
| Platforms supported | All platforms | X/Twitter and Instagram only |
| Cost | Free | Free tier (50/day), Pro removes limit |
| Filtering options | Visual inspection | Keyword, @name, #tag, INVERT (No date filter) |
| Account access required | None (direct login) | None (uses active browser tab) |
| Automation | None | Runs in open tab, no background scheduling |
| Deletion receipt | None | Pro tier provides shareable count receipt |
Who needs which: The manual route is best for users who only need to remove a handful of recent posts and prefer to evaluate each item visually without installing any software. The wyper Social Cleanup extension is designed for users who need to clear hundreds or thousands of old replies, likes, or posts based on specific keywords, but who refuse to grant standing OAuth access to third-party servers.
Agentic browsers like Atlas collect extensive contextual data and store it as memories on remote servers for up to seven days. While you cannot use third-party tools to delete these server-side browser logs, you can control the public social media data the AI reads by cleaning up your profiles. Managing your footprint at the source remains the most reliable way to limit what automated systems learn about your digital history.
The wyper Social Cleanup extension bulk-deletes posts, replies and likes, with filters instead of one tap per post.
The web app installs to your home screen in one tap. No store, no account.
Already using it? ★★★★★ Rate it on the Chrome Web Store. Reviews decide what others get shown first.
 wyper